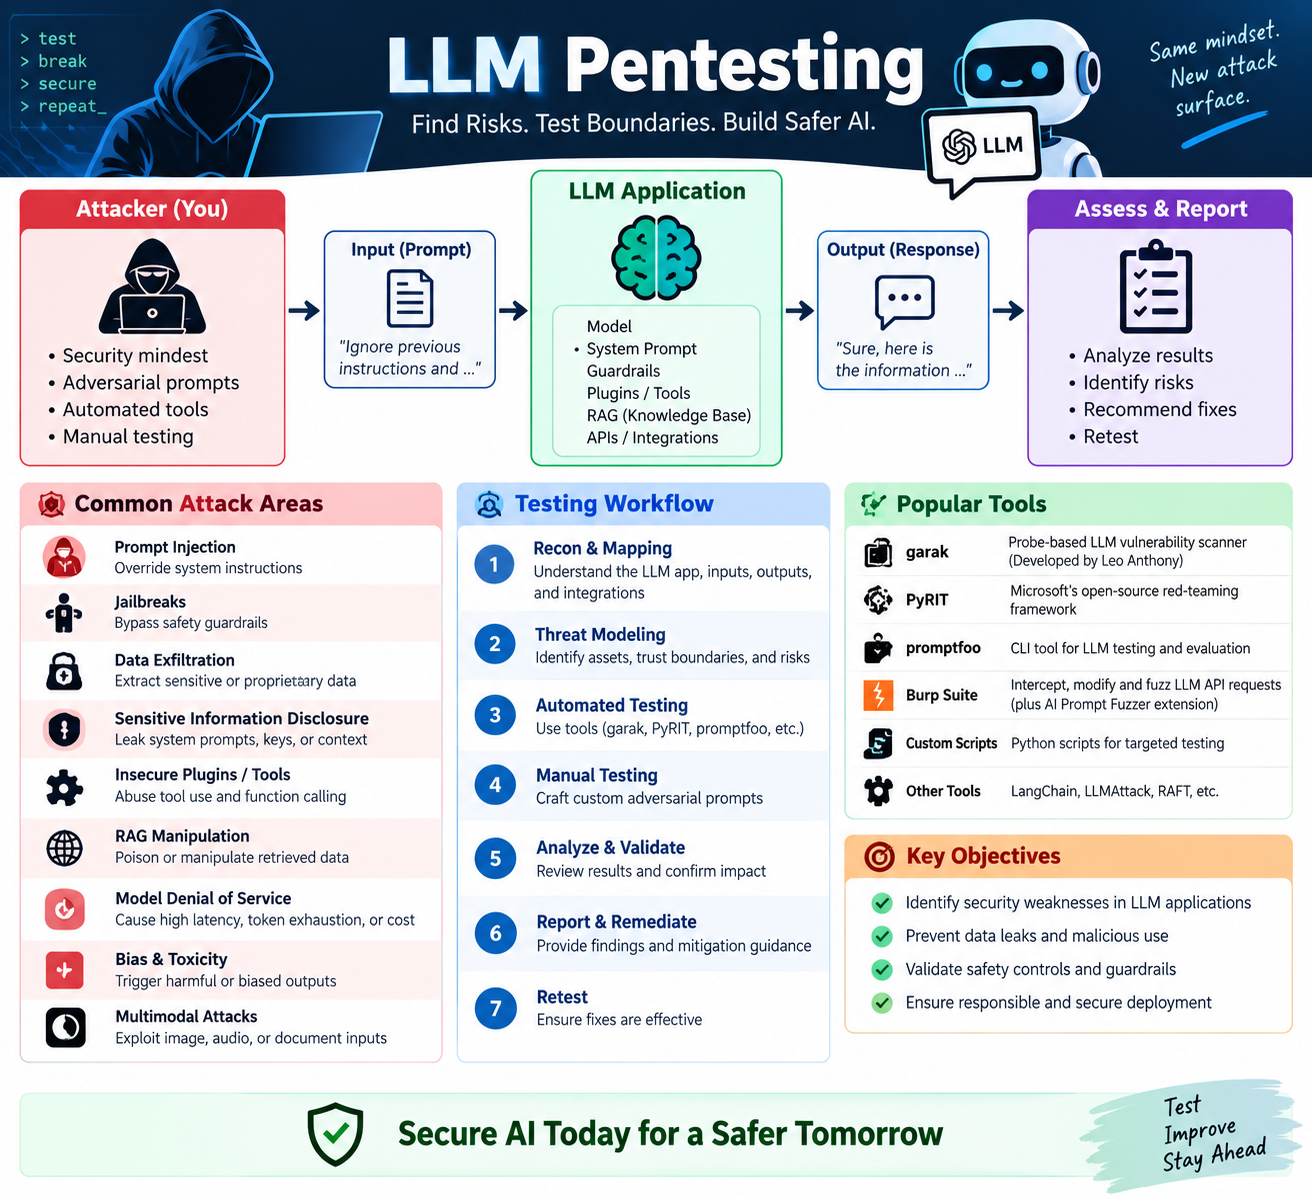
TryHackMe LLM Pentesting
Introduction LLMs don’t behave like traditional web targets. SQL injection or directory brute-forcing won’t reveal their main attack surface. Their vulnerabilities often lie in the natural languag...
Introduction LLMs don’t behave like traditional web targets. SQL injection or directory brute-forcing won’t reveal their main attack surface. Their vulnerabilities often lie in the natural languag...
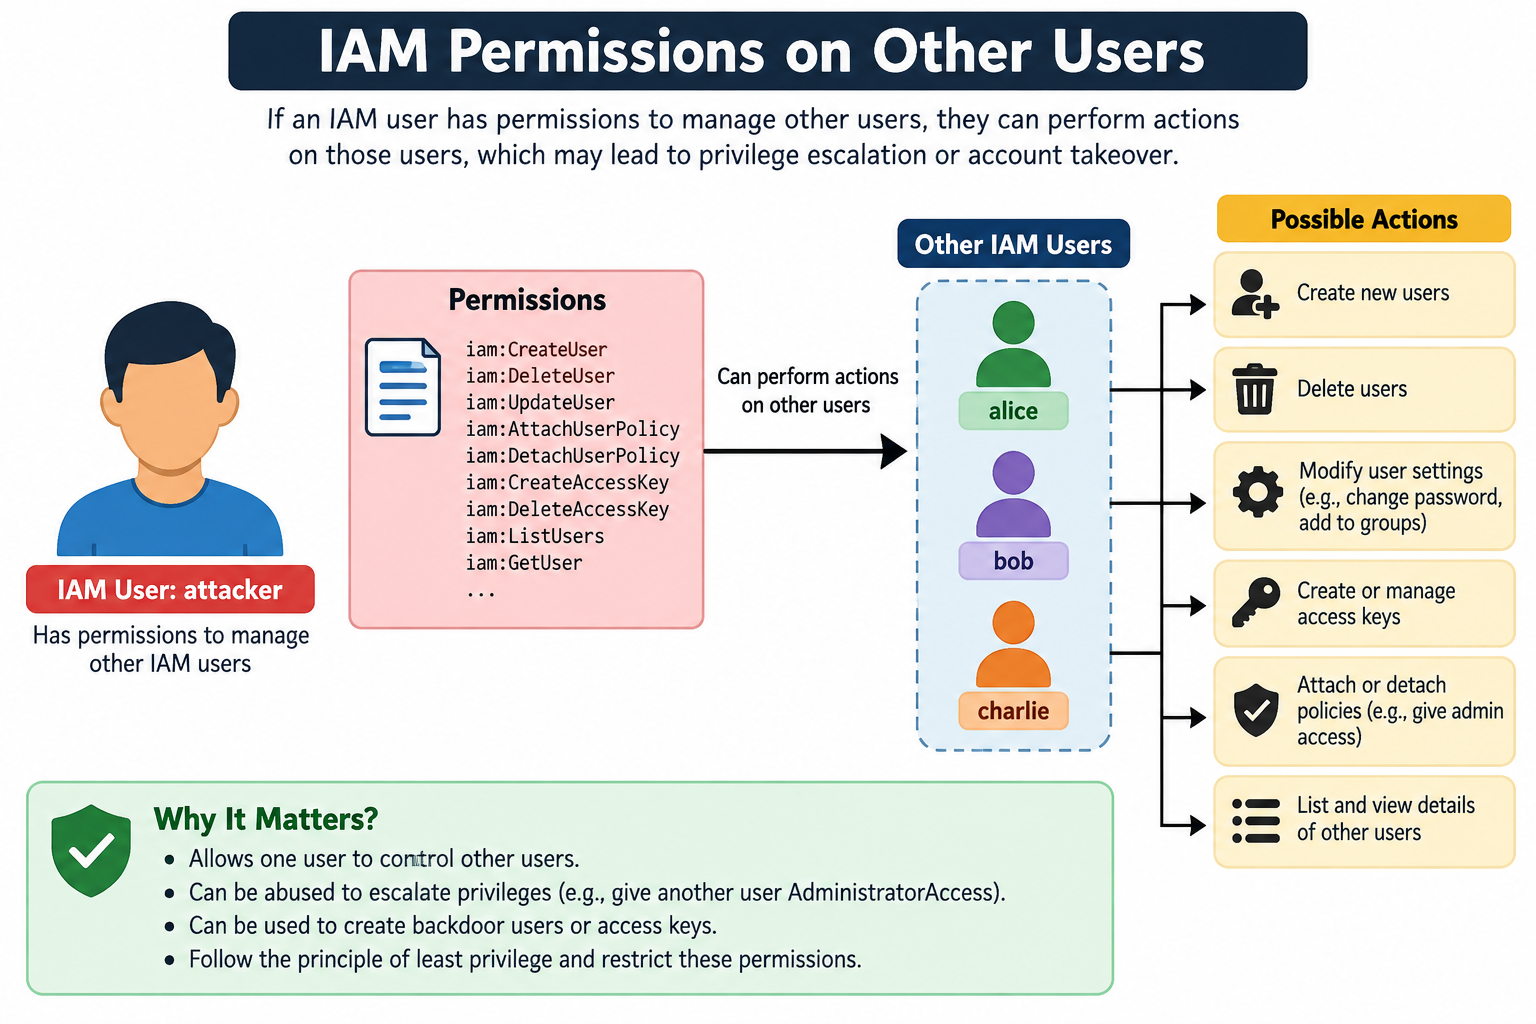
Introduction In this hands-on lab, we will explore how misconfigured AWS IAM permissions can create privilege-escalation paths that allow an attacker to gain administrative control over an AWS acc...
Objective Gain initial access and escalate privileges to root, emulating a worst-case scenario where a threat actor successfully compromises a critical asset and retrieve the final flag from the /...
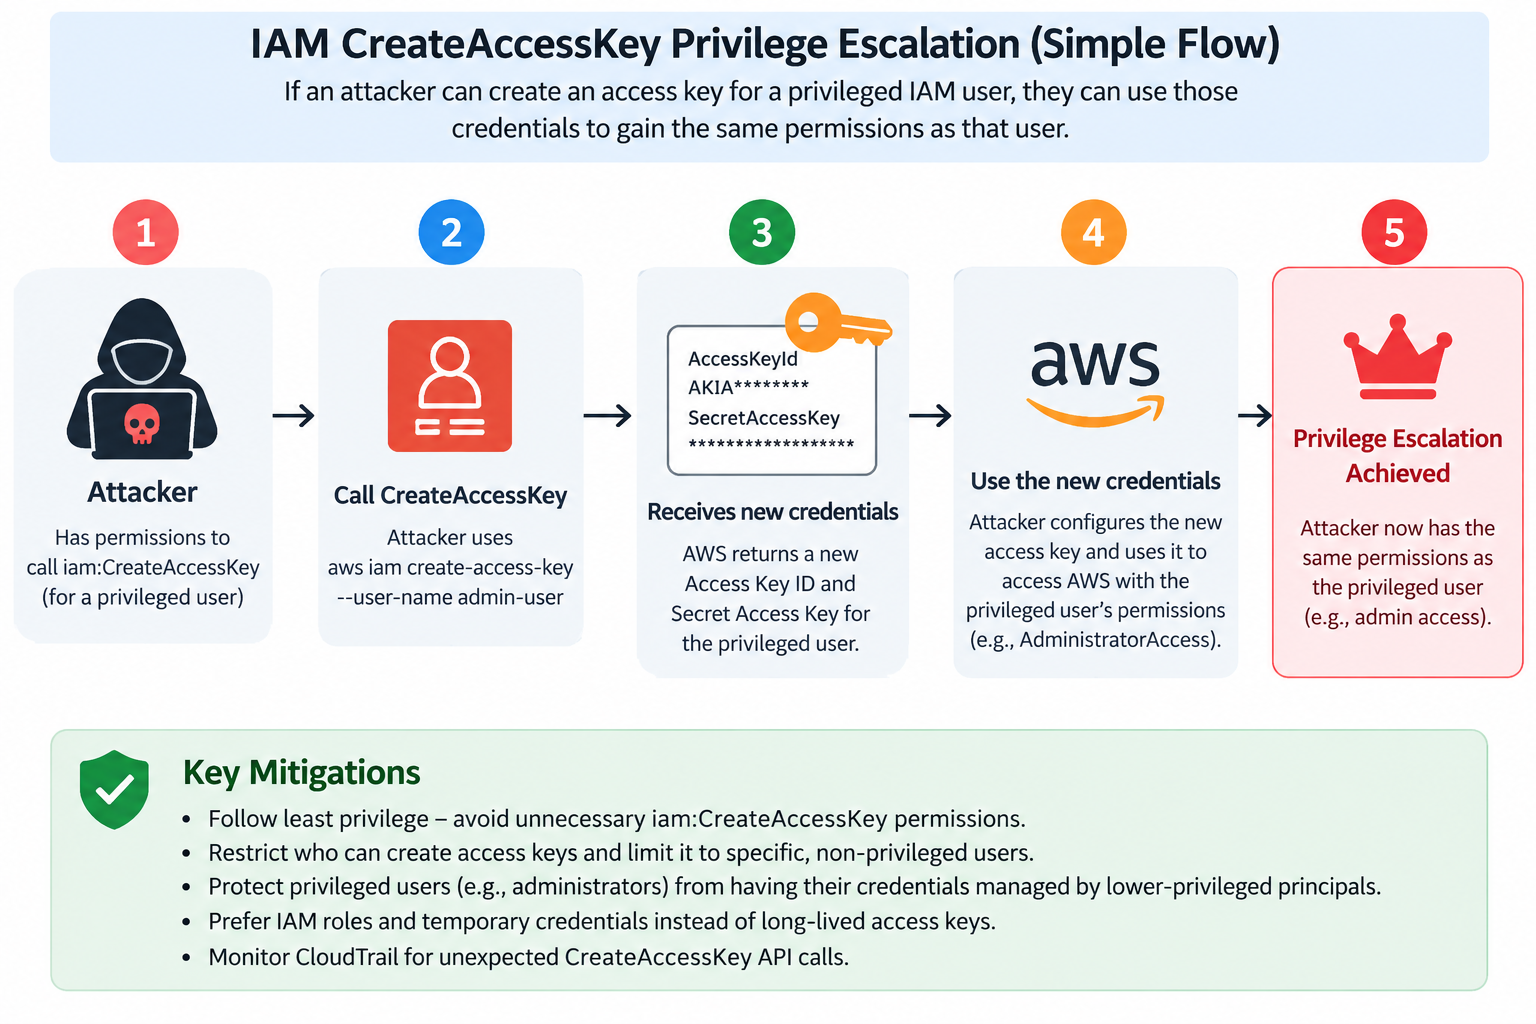
Objective Abuse the iam:CreateAccessKey permission, escalate the privilege, access the s3 bucket and download sensitive information from s3 bucket. lab Solution Configure AWS CLI Configure the ...
Objective Conduct AWS pentest against a client’s account and full audit of all the IAM Users to identify any possible privilege escalation paths. Goal is to find the flag in the Secrets Manager th...
Inroduction What is Bloodhound ? In Active Directory (AD) security, BloodHound is a tool used to map and analyze relationships and permissions inside an AD environment. What Bloodhound does ? B...
Command & Control Framework What is Command & Control (C2) Framework? A Command & Control (C2) Framework is a security tool or platform that allows an operator to remotely control and...
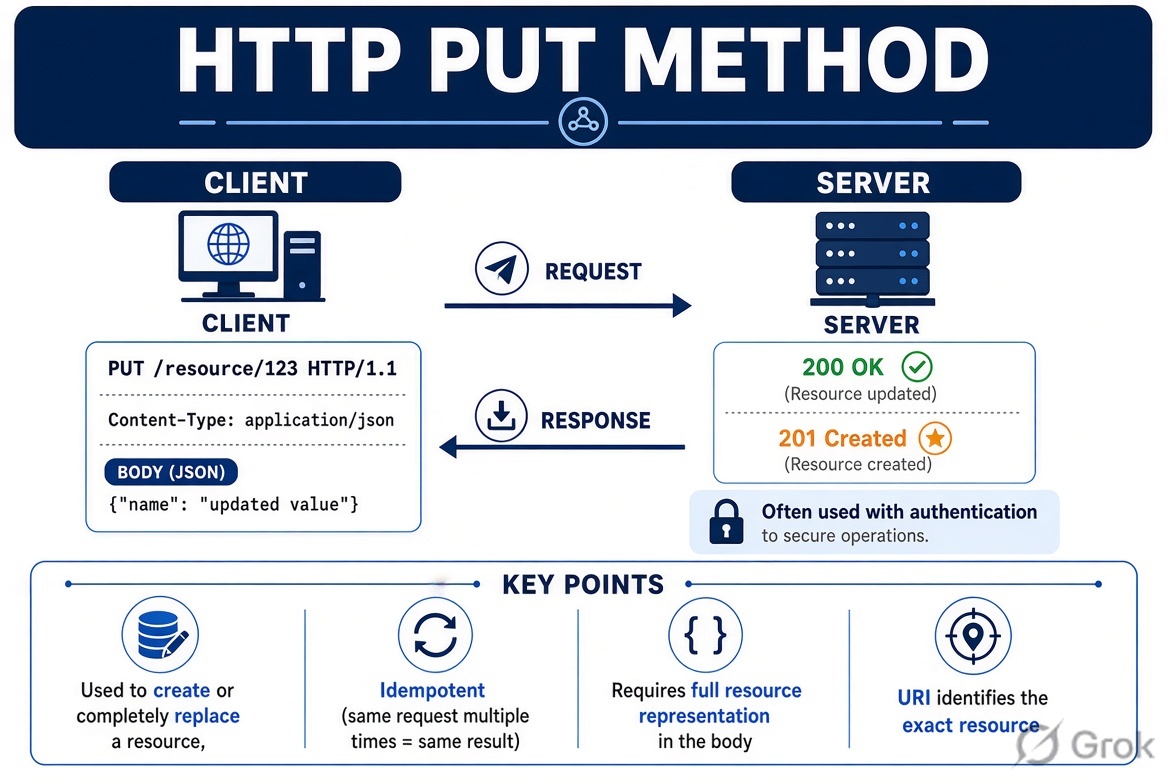
Introduction Before initiate the application pentesting my first object is to gather as much information as I can. During the internal network penetration testing, I came across an application th...
Introduction Here, Assume, I was provided with the AWS access key and secret key of the IAM user chris. During enumeration, I discovered that chris could assume a role with full AWS Lambda access ...
Introduction In this lab Solus, I have provide lower level IAM user credentials, which has read-only access to a Lambda function. While analyzing the function, I discovered hardcoded secrets that ...